 Secure engineering
Offensive security
Build Secure.
Defend Smarter.
Secure engineering & offensive security, from one team
We build custom web, mobile and desktop applications, APIs and backend platforms with security designed in, then test web, API, network and cloud environments from an attacker's perspective. Every finding is proven by hand, scored with CVSS and shipped with a fix that works in your stack.
Core capabilities
- Custom Applications
- API Security
- Network Security
- Cloud Security
- Custom Software
Two disciplines, one team
We it properly, then we try to it
Most organisations buy development from one supplier and security testing from another. The result is predictable: findings the development team cannot act on, and applications built without the context of how they will be attacked. BastionWolf does both, so neither side loses that context.
Engineers who test. Security testers who build.
The same team that writes production code also breaks it. Findings come with a fix that fits your stack, not a generic recommendation.
Manual testing, not just scanning
Automated tooling maps the attack surface. Business-logic flaws, broken access control and chained exploits are found by hand.
Security built in, not bolted on
Threat modelling, secure defaults and authorisation design happen during architecture, before they become expensive to change.
Reports your team can act on
Reproduction steps, evidence, CVSS-based severity and remediation guidance written for developers as well as for management.
Services
Development and offensive security
Engagements range from a single application test to building and maintaining a platform end to end. Every one starts with a scoping conversation, not a quote generator.

Custom Application Development
Purpose-built web, mobile and desktop applications designed, delivered and hardened by security-minded engineers.
Learn more Offensive SecurityWeb Application Penetration Testing
Manual, authenticated testing of your web application against the way real attackers approach it.
Learn more Offensive Security
API Penetration Testing
Authorisation-focused testing of REST, GraphQL and internal APIs, guided by the OWASP API Security Top 10.
Learn more Offensive Security
Network Penetration Testing
External and internal network testing that establishes how far an attacker could actually get.
Learn more Offensive Security
Cloud Penetration Testing
Configuration and identity review of AWS, Azure and GCP environments, combined with hands-on attack-path testing.
Learn more Offensive SecurityVulnerability Assessment
Broad, repeatable coverage of your estate with the noise removed and the results prioritised.
Learn moreSelected projects
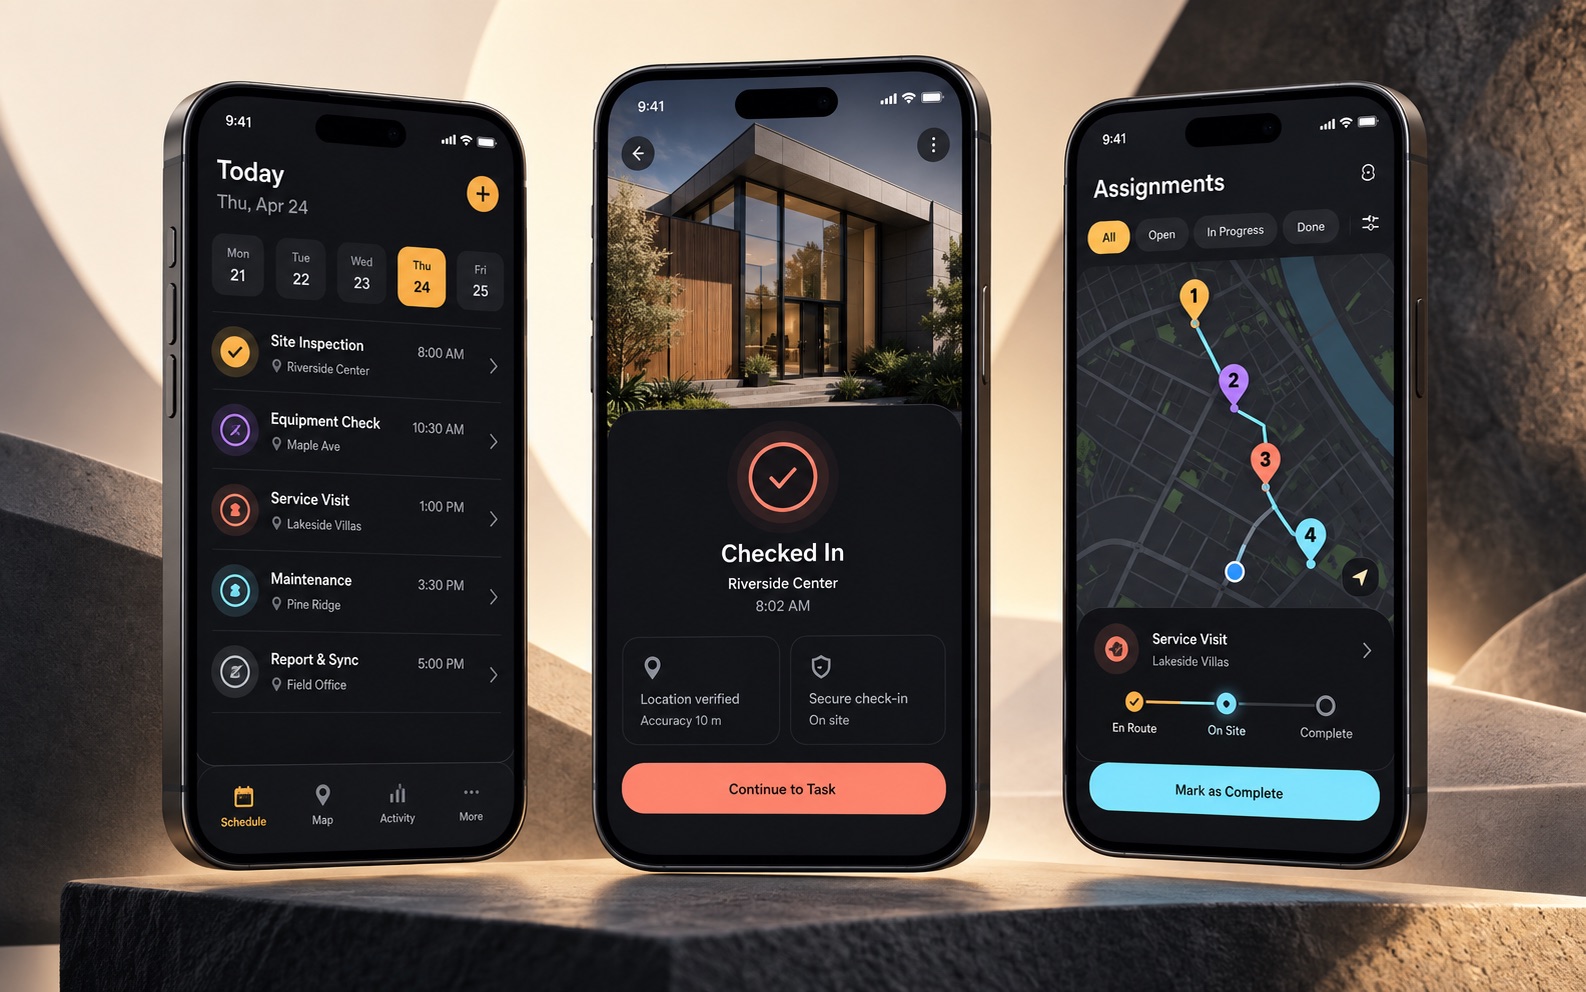
Selected projects, shown in detail
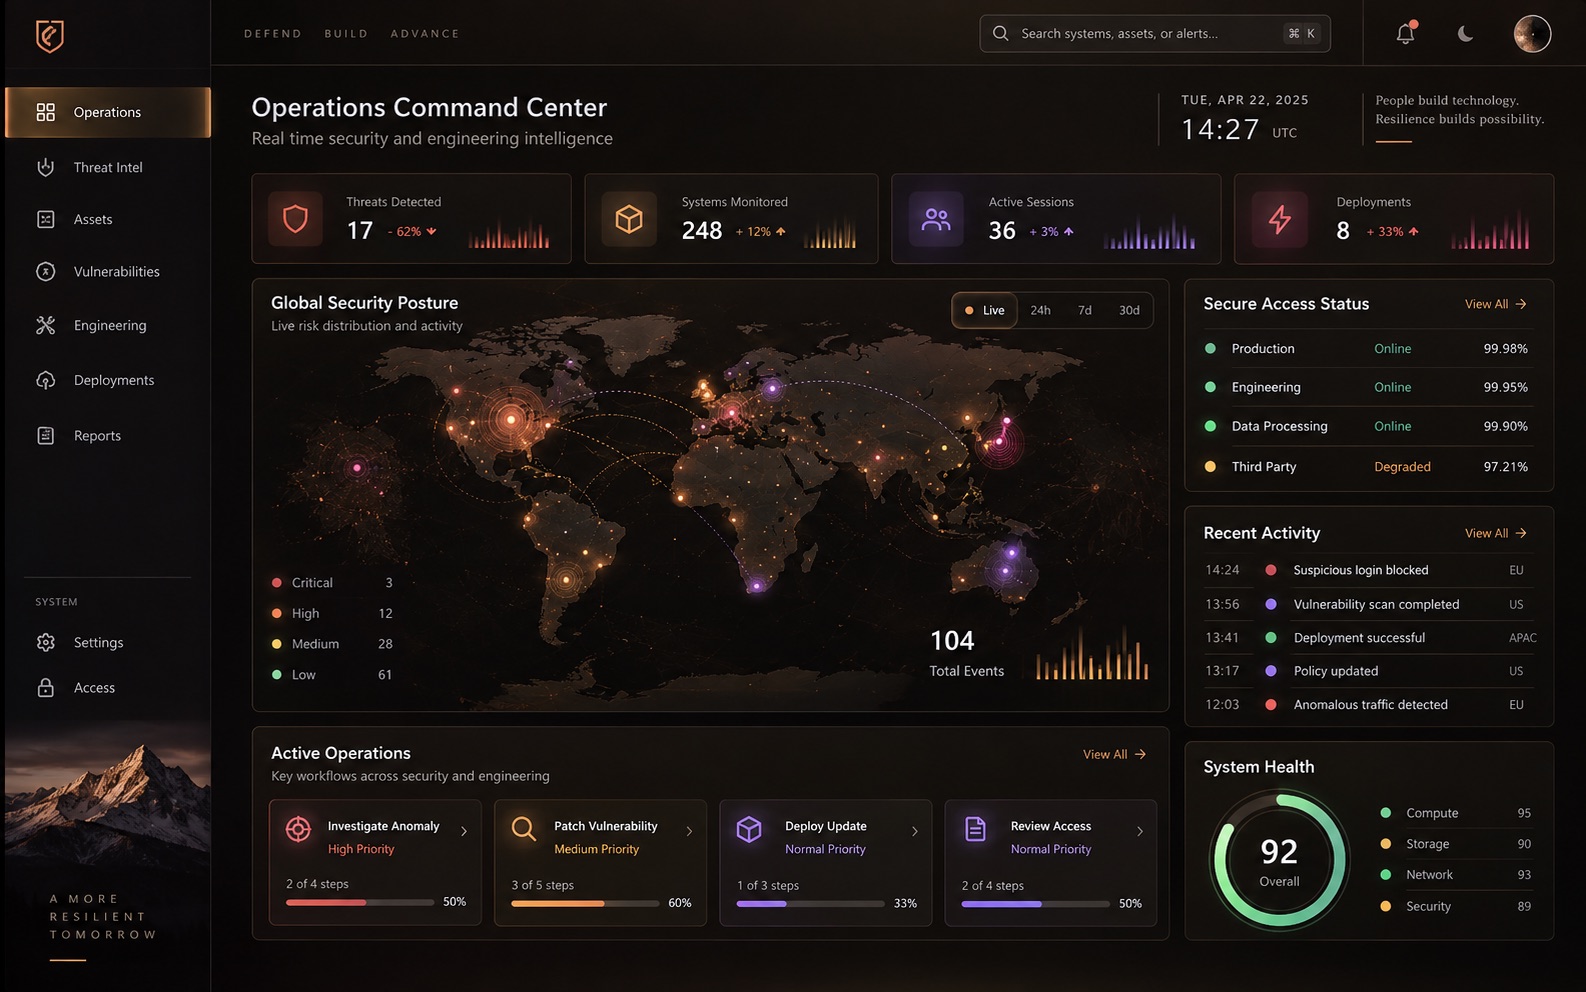
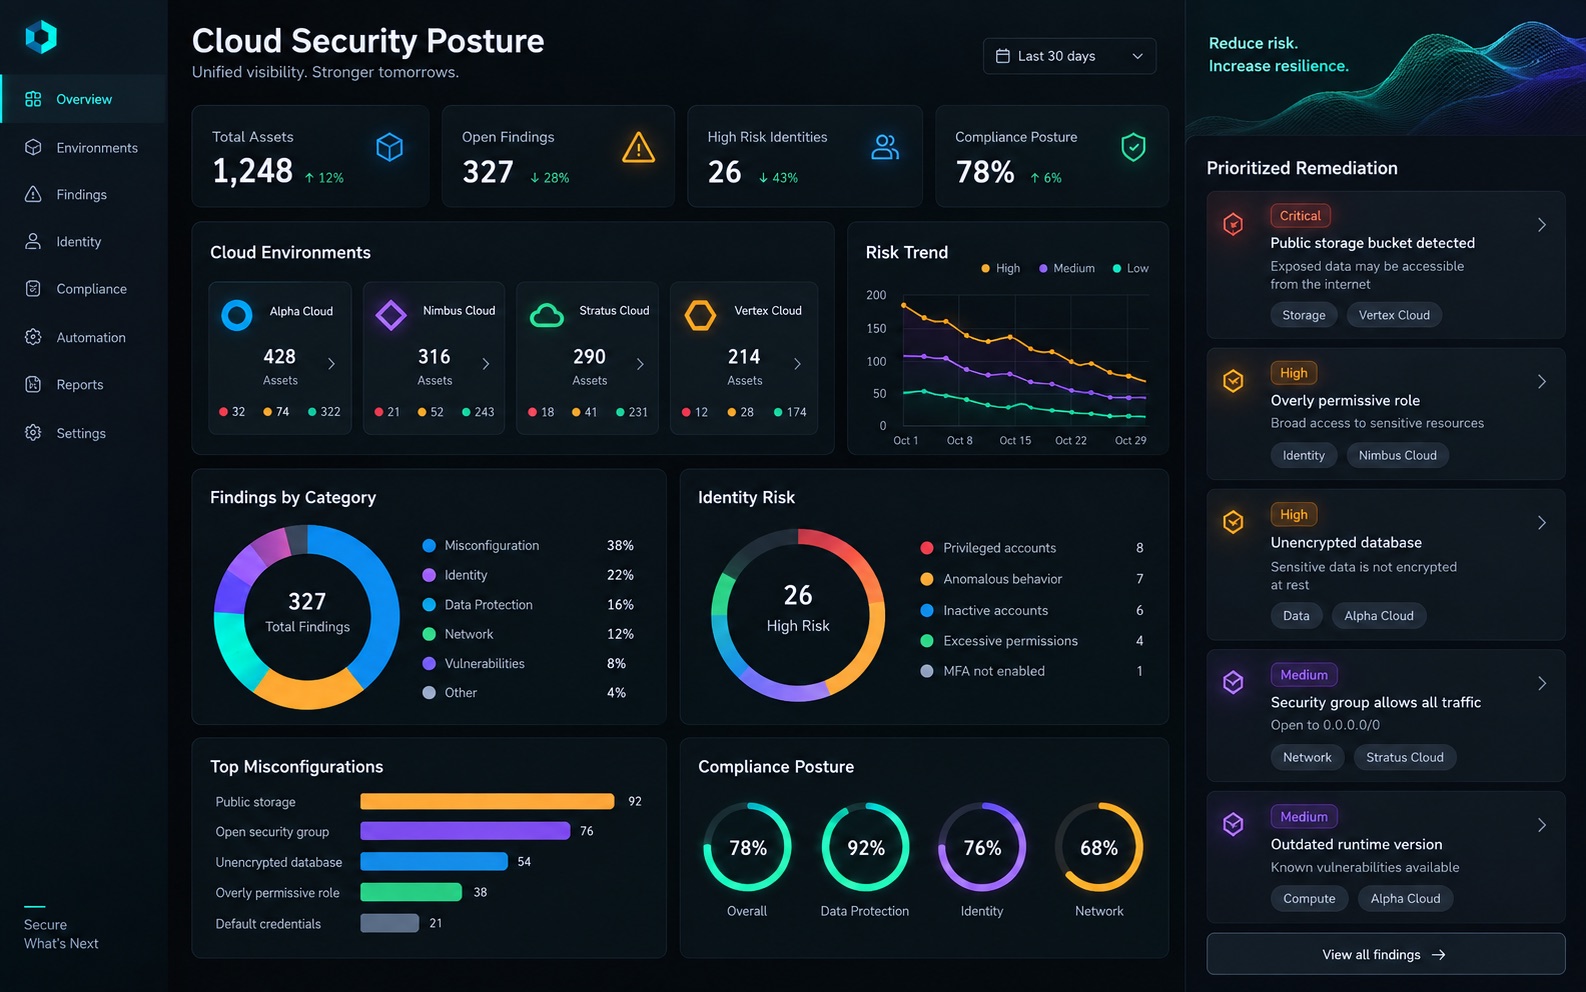
See how requirements become secure, usable products through project outcomes, interface previews and walkthroughs.
Security methodology
Testing that reflects how systems are actually attacked
Scanners establish the baseline. Everything that matters, including broken access control, business logic abuse, chained exploitation, privilege escalation is found by hand.
Our testing follows recognised methodologies including the OWASP Web Security Testing Guide, the OWASP API Security Top 10, PTES and NIST SP 800-115, with severity communicated using CVSS alongside a plain statement of impact in your environment.
Included as standard
Every engagement guarantees
- Written authorisation and an agreed scope before any testing begins
- Manual verification of every reported finding
- Reproduction steps and captured evidence per issue
- Immediate notification of critical findings, not held for the report
- Remediation guidance written for the developers who will fix it
- A retest of fixed findings, included
Engagement process
From first call to confirmed remediation
A predictable process with clear checkpoints. You always know what is happening, what has been found and what happens next.
-
Scoping call
We agree on targets, environments, testing windows, constraints and the outcome you need. No testing begins before this is written down.
-
Authorisation & rules of engagement
Written authorisation, contact escalation paths, out-of-scope systems and handling rules for any data encountered.
-
Execution
Testing or development runs against the agreed scope with regular progress updates. Critical findings are reported immediately, not held back for the final report.
-
Reporting
An evidence-backed report with an executive summary, technical detail, severity ratings and prioritised remediation guidance.
-
Remediation support & retest
We work with your developers through the fixes, then retest the affected issues and confirm closure.
How we operate
Principles we do not trade away
Authorised testing only
Every engagement runs under written authorisation and an agreed scope. We will not test systems you do not own or cannot authorise.
Least data handled
We access only what is needed to demonstrate impact, avoid bulk data extraction, and return or destroy engagement data on request.
Evidence over assertion
Findings are backed by reproducible steps and captured evidence so your team can verify them independently.
Clear, honest communication
Plain-language severity, realistic exploitability, and no inflated risk ratings used to pad a report.
Ready to find the weaknesses first?
Tell us what you are building or what you need tested. We will come back with a scope, a timeline and a clear price, with no obligation.